Multi-Tenant Architecture: What It Is and Why It Matters

Multi-tenant architecture is a software design pattern that lets one application instance serve multiple customer organizations while keeping each tenant's data separate. This article covers the three main database isolation models, how to choose between them based on compliance and performance requirements, and the security practices that prevent cross-tenant data leaks. You'll also learn why the rise of AI agents makes isolation failures more consequential than before.
Key takeaways
Here are the main points to keep in mind as you evaluate multi-tenant architecture:
- Definition: Multi-tenant architecture is a software design where one application instance serves multiple separate customer organizations, called tenants, from shared infrastructure.
- Core tradeoff: You gain significant cost savings and operational simplicity by sharing resources, but you accept responsibility for enforcing strict logical boundaries between tenants.
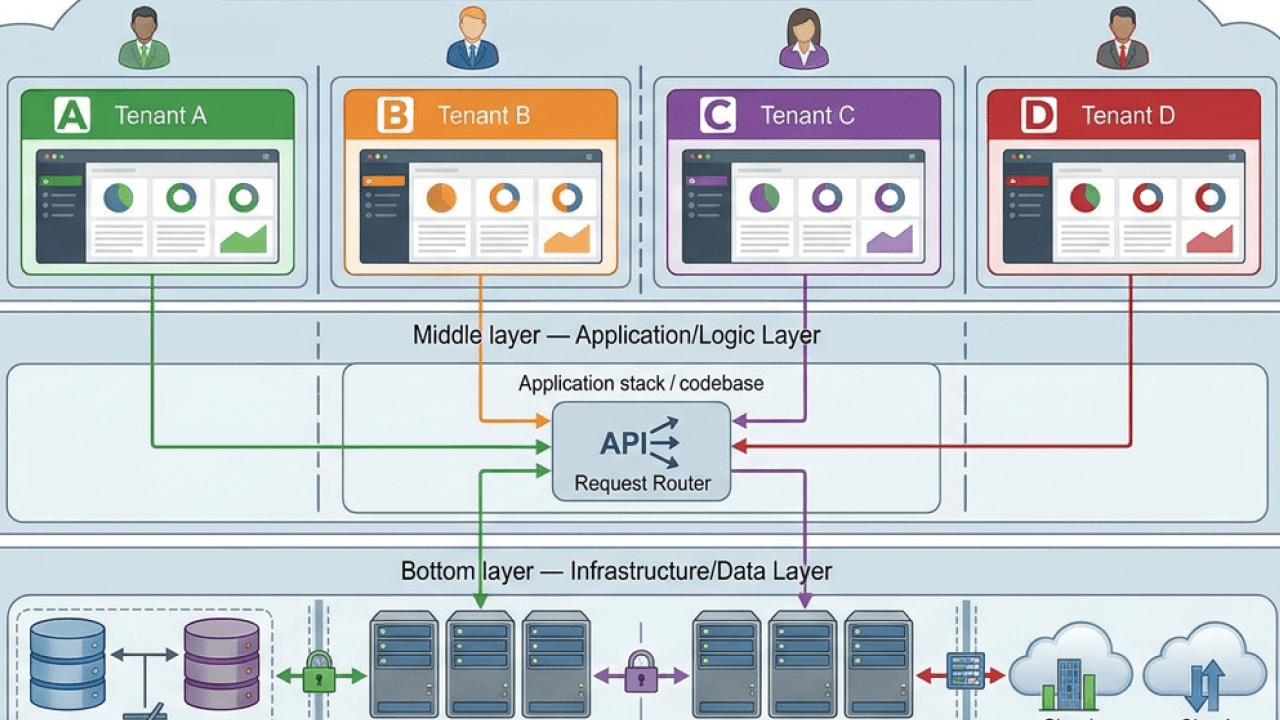
- Stack placement: Tenancy decisions affect three layers (application, database, and infrastructure) and each layer requires its own isolation strategy.
- Misconception: Multi-tenant is not the same as multi-user. People sign in with individual accounts; tenants are organizational boundaries that contain those accounts.
- AI relevance: As organizations deploy AI agents that access tenant data, isolation failures carry higher stakes because an agent with cross-tenant visibility could surface sensitive information in the wrong context.
What is multi-tenant architecture?
A single application instance. Hundreds of companies. Each one sees only their own data.
That's multi-tenancy at work, and it shows up across three layers. At the application layer, the software identifies which tenant is making each request. At the database layer, you decide how to store and separate each tenant's records. At the infrastructure layer, compute and storage resources are pooled or dedicated based on your isolation requirements.
Two concepts help clarify how this works in practice:
- Control plane: Handles tenant provisioning, billing, and global configuration across the entire system.
- Data plane: Where tenant data actually lives and gets processed during normal operations.
People often confuse tenancy with related concepts. Multi-tenant is not the same as multi-user. A single-tenant application can have thousands of people with accounts, but tenants represent organizational boundaries. Multi-tenancy does not require a shared database either; you can run separate databases for each tenant while still sharing the application layer. And while embedded analytics products almost always need multi-tenant foundations, they're a use case built on top of this architecture, not the architecture itself.
{{custom-cta-1}}
Multi-tenant architecture models
Get this decision wrong and you will spend years paying for it. The database model you choose determines your isolation guarantees, operational complexity, and cost trajectory. Migrations between models are notoriously painful.
Shared database, shared schema
All tenants share the same tables. A tenant_id column distinguishes records.
This is the most cost-efficient approach and works well when tenant data volumes are similar and compliance requirements do not mandate physical separation. If any tenant needs dedicated encryption keys or if noisy-neighbor risk violates your service-level agreements (SLAs), look elsewhere. Assuming shared-schema automatically means weaker security? That's wrong. With proper row-level security and tenant context enforcement, this model can meet rigorous compliance standards. The isolation is logical rather than physical, but that does not make it less effective when implemented correctly.
Shared database, separate schemas
Each tenant gets its own schema within a shared database instance. You get stronger logical isolation and simpler per-tenant backup and restore, but schema management overhead increases. This fits mid-market SaaS teams that need clear boundaries without the cost of separate database instances.
Separate databases
Maximum isolation. Simplest compliance story. Highest cost.
Choose this when contracts require physical data separation, data residency laws demand geographic isolation, or tenant workloads vary so dramatically that sharing resources becomes impossible.
Hybrid models
Many production systems combine approaches. Smaller customers share a pooled environment while enterprise accounts get dedicated databases. This creates a graduation pattern where customers start in the shared pool and migrate to dedicated resources as usage or contract tier increases.
{{custom-cta-2}}
Data isolation and database design for multi-tenancy
Cross-tenant data leaks can violate compliance policies, damage customer trust, and trigger regulatory action.
Tenant identity and context
Isolation starts before any query hits the database. When someone logs in, the identity provider issues a token with tenant claims. Application middleware extracts that context and scopes the database session to that specific tenant.
If any link in this chain breaks? A missing claim, a misconfigured middleware, a session that doesn't propagate correctly. Queries can return data from the wrong organization.
Tenant context has to be a platform primitive. Not something bolted on before launch.
Authorization and role-based access control
Role-based access control works differently in shared environments. Roles exist within tenant boundaries, so an admin in Tenant A has zero visibility into Tenant B. You need to map roles to tenant identifiers to prevent horizontal privilege escalation. Access control alone won't secure the system; it has to combine with verified tenant context.
Row-level security
For shared-schema models, row-level security policies enforce tenant boundaries at the database engine level. A Postgres policy might filter all queries by the current session's tenant_id. This acts as defense-in-depth, but it can't replace application-level checks. If the application sets the wrong tenant context, the database will enforce the wrong boundary.
In practice, background jobs cause the most dangerous leaks. The main API might handle tenant context perfectly, but a reporting job that forgets to scope its queries can email one customer's data to another.
Failure modes to check for:
- Missing tenant_id on a new table, leaving data visible to everyone
- Tenant context not propagating to background jobs
- Search indexes lacking tenant scopes
- Cache keys missing tenant prefixes
- Logs containing sensitive data without tenant labels
Single-tenant vs multi-tenant architecture
This choice shapes pricing models, operational burden, and how fast new features reach customers.
Infrastructure model
Single-tenant gives each customer dedicated compute, storage, and sometimes network infrastructure. Multi-tenant shares infrastructure while isolating at the application or database layer. Single-tenant offers maximum isolation but multiplies infrastructure management by customer count.
Cost structure
Single-tenant costs scale linearly. Every new customer adds infrastructure.
Multi-tenant? The marginal cost per customer decreases as the tenant base grows. For vendors with high customer counts, shared architecture is dramatically more efficient. For vendors serving a handful of high-value enterprise accounts, dedicated infrastructure can make sense.
Customization flexibility
Single-tenant allows deep per-customer customization at the infrastructure level (custom integrations, dedicated resources, unique configurations). Multi-tenant requires customization through configuration rather than code forks: feature flags, tenant-specific settings, tiered capabilities.
Multi-tenant architecture is the default for SaaS products at scale.
How to choose a multi-tenant architecture
Compliance requirements usually determine the minimum viable isolation level. Cost optimization happens after those baselines are met.
Compliance requirements
The Health Insurance Portability and Accountability Act (HIPAA) requires audit trails and access controls but does not explicitly mandate physical separation. The General Data Protection Regulation (GDPR) can introduce data residency requirements that push teams toward regional sharding or per-tenant databases for European customers. Service Organization Control 2 (SOC 2) requires demonstrable access controls and audit logging, which can work with any tenancy model as long as controls are documented.
If any customer segment requires physical separation, plan for hybrid tenancy from day one.
Performance and SLAs
Noisy-neighbor risk increases with shared resources. If SLAs guarantee specific latency or throughput, evaluate whether a shared model can deliver under peak load. Quotas and rate limiting help mitigate noisy-neighbor effects. Dedicated resources eliminate the risk at higher cost.
Growth and scale
Early-stage products often start with shared-schema models for speed and cost efficiency. As enterprise deals arrive, the architecture needs to support graduation to dedicated resources. Design for this migration path early: treat tenant context as first-class, maintain clean boundaries, and build tooling for tenant-level backups.
A practical test: if completely purging a single tenant's data requires manual database queries or takes more than a few minutes, your isolation boundaries are probably too porous.
Multi-tenant architecture pros and cons
Cost efficiency
Shared infrastructure means lower per-tenant costs, faster provisioning, and centralized operations. Updates ship once and apply to all tenants. Operational burden scales sub-linearly with customer count.
Isolation risk
Shared resources create shared fate.
A bug, breach, or resource exhaustion in one tenant can affect others. The blast radius is larger than in single-tenant deployments. As more organizations roll out AI agents that access tenant data, isolation failures carry higher consequences. An agent with cross-tenant visibility could surface sensitive information in the wrong context.
Best practices for secure multi-tenant SaaS
Most cross-tenant data leaks are not caused by sophisticated attacks. They happen because a developer forgot tenant context in a query, an unscoped cache served wrong data, or a background job forgot which organization it was processing.
Tenant context as a platform primitive
Inject tenant context at the edge and propagate it through every layer: API gateway to application to database to background jobs to logs. If tenant context is optional or inconsistent, isolation will eventually fail.
Treat tenant_id as a required field. Never nullable.
Teams sometimes assume that setting tenant context at the API layer is sufficient, but context must be explicitly passed to every downstream service, queue, and scheduled job. It does not inherit automatically.
Least-privilege access
Apply least-privilege at every layer. Database credentials should be scoped to minimum necessary permissions. Application roles must be tenant-scoped. API tokens should carry tenant claims. Avoid shared service accounts with cross-tenant visibility.
Isolation tests at every layer
Code review alone cannot verify isolation. Build automated negative tests: attempt to access Tenant B's data while authenticated as Tenant A. The request must fail. Test at the database layer with row-level security policies, at the API layer with authorization checks, and at the UI layer to ensure no cross-tenant data appears in responses.
The more dangerous threat in shared environments is Insecure Direct Object Reference (IDOR), where someone iterates through URL parameters to view another tenant's records. You'll notice this attack vector gets overlooked in security audits that focus on authentication rather than authorization boundaries. Automated test suites need to verify this continuously.
Verification checklist:
- Tenant context propagates to all queries, including background jobs
- Row-level security policies verified with negative test cases
- Cache keys prefixed with tenant identifier
- Search indexes scoped to prevent cross-tenant leakage
- Audit logs include tenant_id on every entry
- Per-tenant encryption keys integrate with key management where required
How Domo supports multi-tenant data and analytics
Domo is an agentic platform for the intelligent enterprise that helps teams run governed, tenant-aware analytics and AI workflows across business units, customers, or partners.
At the Foundation layer, Domo helps make data AI-ready by connecting to your existing cloud data platform and enforcing governance (including role-based access control and row-level security). At the Activation layer, Domo's AI agents operate with bounded autonomy, with human-in-the-loop oversight, so people can set objectives and constraints while the system executes within guardrails. At the Distribution layer, outcomes can be delivered into the workflows people already use, including embedded experiences and automated processes.
Domo is unified by design, modular by adoption. Teams can start with a single entry point and expand over time, reusing the same governed definitions and controls across tenants.
If you're ready to pressure-test tenant isolation before AI agents expand access across more systems, Watch a demo.